Recover From Cyber Incidents in Minutes
Firefly delivers cyber resilience by automatically recovering complete applications and infrastructure within minutes after cyber incidents. Recognized by Gartner as a leading Cloud Application Infrastructure Recovery Solution (CAIRS).
Your Security Stack Detects the Attack, but It Can’t Rebuild What Was Destroyed
EDR, SIEM and SOAR are built to detect and contain, not to rebuild. When an attack succeeds, the gap between detection and recovery exposes your business to weeks of downtime, regulatory penalties and reputational damage.
Full production often takes weeks to restore after a cyberattack. The data survives, but the infrastructure can't be rebuilt by hand fast enough under pressure.
There's a category of risk your security stack doesn't cover: Infrastructure Recoverability. Firefly covers it.
Most Teams Recover Into the Breach. Firefly Recovers Out of It.
Clean-region Recovery
Rebuilding into an isolated account the attacker can't reach
Immutable IaC Snapshots
Point-in-time infrastructure code that can't be encrypted or corrupted by ransomware
Continuous Posture Validation
Knowing your recovery environment is actually clean and ready before you need it
How Firefly Delivers Cloud Cyber Resilience:
From Posture to Recovery
Cloud Application Infrastructure Recovery Solution
CAIRS
Enable ransomware-safe rollback and clean-region recovery
Quickly restore operations in minutes, not hours
Recover full environments, not partial services
Get versioned IaC snapshots that ransomware can't encrypt or corrupt
Meet RTO and RPO requirements, with RTO under 1 hour
Recover AI agents whole, with everything they need to work
Continuously map dependencies for every critical service, through direct API discovery across clouds, identity, SaaS and AI agents
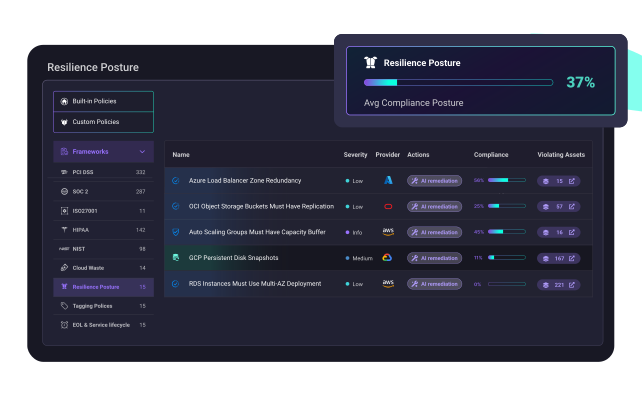
Cloud Resilience Posture Management
CRPM
Get real-time view of cyber recovery readiness across all environments
Expose single points of failure across clouds and regions
Validate backups, failover paths, RTO and RPO for every service, including third-party dependencies
Replace annual tabletop exercises and manual DR projects with scheduled, full-stack recovery tests
Get audit trails mapped to DORA, NIS2, SOC 2, ISO 27001, HIPAA, CRA and PCI-DSS
What Your Business Gains
CRPM exposes and closes recovery gaps before an attack, and CAIRS rebuilds your infrastructure cleanly when one strikes
Recover Into a Clean Environment in Minutes, Not Weeks
Rebuild your full cloud environment into a clean, isolated region or account the attacker can't reach. Roll back to any point-in-time state before the breach from immutable, versioned IaC snapshots, and meet RTO under 1 hour, even during active cyberattacks.
Know Your Cyber Recovery Posture Before the Attack Finds It
Get a real-time view of what is protected, what is not, and whether your environment can be rebuilt during an incident. Validate backups, replication, dependencies, and failover paths across clouds, regions, and accounts — continuously, not just at audit time.
Eliminate Hidden Risks Before They Become Attack Surface
Uncover the blind spots security tools miss: risky dependencies, unreplicated resources, drift and unmapped agentic infrastructure. Replace once-a-year tabletop exercises with scheduled, full-stack recovery tests in an isolated environment, and feed every result back into your recovery plan.
Prove Recovery Readiness to Every Regulator. Automatically.
Give your board a clear view of resilience: readiness scores, single points of failure and tested RTO for every critical service. Audit trails and compliance posture are mapped to DORA, NIS2, HIPAA, the EU Cyber Resilience Act, SOC 2, ISO 27001 and PCI-DSS, ready the moment an auditor asks.
Recognition